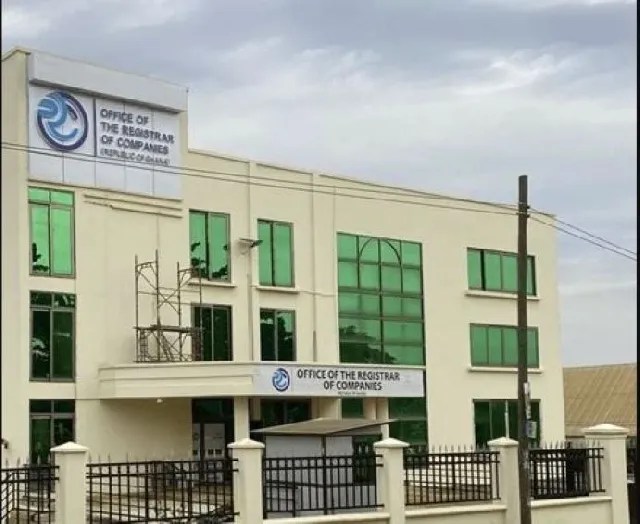
When Cybersecurity Meets Accountability: A Lesson in Digital Governance
Let’s start with a question: Why should we care when a government agency gets fined for cybersecurity negligence? Because in our hyperconnected world, the answer reveals everything about how seriously institutions treat the digital trust we place in them. Ghana’s recent crackdown on the Office of the Registrar of Companies (ORC) and Purpleline Solutions offers a masterclass in regulatory enforcement—and human folly.
The ORC’s Costly Shortcut
Here’s the bare-minimum summary: ORC, a critical government body handling corporate registrations, outsourced cybersecurity to an unlicensed firm. The result? A GH¢240,000 fine. But this isn’t just a bureaucratic footnote. Personally, I think this case exposes a dangerous mindset: treating cybersecurity as a checkbox exercise rather than a strategic imperative. ORC had explicit instructions to hire Tier 1 licensed providers. Instead, they opted for convenience over compliance. Why? Either arrogance, incompetence, or—most worryingly—a culture where rules are seen as optional until enforcement bites.
Purpleline’s Misguided Gamble
Let’s not let Purpleline off the hook. They knowingly operated without a license, racking up a GH¢120,000 penalty. But here’s what fascinates me: Their post-hoc license application. Did they think regulators wouldn’t notice? Or did they assume bureaucracy moves too slowly to matter? This reflects a broader issue in tech contracting—companies often bet on enforcement lagging behind execution. Spoiler: It rarely does. The CSA’s swift action here sends a clear message: “We’re watching, and we’re not playing games.”
The Real Story: Regulatory Teeth
The Cyber Security Authority (CSA) didn’t just slap wrists—they weaponized Section 92 of Ghana’s Cybersecurity Act. Why does this matter? Because too many regulators talk tough and do little. The CSA’s approach—public shaming via detailed statements, strict timelines for compliance, and fines tied to penalty units—shows they’ve studied enforcement psychology. They’re leveraging transparency as a deterrent. A detail I find especially interesting: The CSA explicitly states that “an application is not a license.” This closes a loophole where firms might test boundaries by starting work before approval. It’s regulatory hardball with a pedagogical edge.
Beyond Ghana: A Global Canary in a Coal Mine
Zoom out, and this incident mirrors a universal tension. Governments worldwide are scrambling to secure critical infrastructure while balancing operational efficiency. ORC’s mistake isn’t unique—it’s a symptom of a system where cybersecurity competes with budgets, timelines, and political priorities. What many people don’t realize is that these breaches often stem from organizational inertia, not technical naivety. The real vulnerability isn’t firewalls; it’s human decision-making.
The Bigger Picture: Trust in the Digital Age
Let’s connect this to a deeper trend: Digital governance as a proxy for institutional integrity. When a registry of companies—the very foundation of economic transparency—fails basic cybersecurity hygiene, it erodes confidence in the entire system. Imagine foreign investors reading about this fine. Do they think, “Ah, a one-off mistake,” or “What else are they getting wrong?” The CSA’s crackdown isn’t just about punishment; it’s damage control for national reputation in an era where digital competence equals competence, period.
Final Thoughts: The Price of Neglect
Is GH¢240,000 enough to change behavior? Maybe not. But the reputational sting here outlasts the financial penalty. This case will haunt procurement meetings for years—a cautionary tale of what happens when corners get cut. If you take a step back, the bigger question isn’t about fines but culture. How do we build systems where compliance isn’t reactive but ingrained? Ghana’s cybersecurity authority has drawn a line. Whether others respect it depends on whether they fear the consequences—or finally value security as much as they claim.